

100% Accurate Answers! Jun-2026 SC-300 Actual Real Exam Questions
Best Value Available! 2026 Realistic Verified Free SC-300 Exam Questions
The SC-300 exam covers a range of topics related to identity and access management, including designing and implementing identity solutions, managing access and authentication, securing identities and access, and monitoring and reporting on identity and access activities. Candidates will need to demonstrate their knowledge and skills in these areas through a combination of multiple-choice questions, case studies, and other types of assessments.
To prepare for the Microsoft SC-300 exam, candidates are recommended to have hands-on experience with Azure AD and Azure services, as well as a deep understanding of identity and access management concepts. Microsoft offers a range of training resources, including instructor-led courses, self-paced online training, and practice exams, to help candidates prepare for the exam. Passing the Microsoft SC-300 exam validates the candidate’s expertise in identity and access management and demonstrates their ability to effectively manage identity and access solutions in Microsoft Azure. Microsoft Identity and Access Administrator certification is highly valued by employers and can help individuals advance their careers in the field of cloud-based identity and access management.
NEW QUESTION # 101
You have a Microsoft 365 tenant named contoso.com.
Guest user access is enabled.
Users are invited to collaborate with contoso.com as shown in the following table.
From the External collaboration settings in the Azure Active Directory admin center, you configure the Collaboration restrictions settings as shown in the following exhibit.
From a Microsoft SharePoint Online site, a user invites [email protected] to the site.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 102
You have a Microsoft 365 tenant.
You configure a conditional access policy as shown in the Conditional Access policy exhibit. (Click the Conditional Access policy tab.)
You view the User administrator role settings as shown in the Role setting details exhibit. (Click the Role setting details tab.)
You view the User administrator role assignments as shown in the Role assignments exhibit. (Click the Role assignments lab.)
For each of the following statement, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Yes
Yes
No
NEW QUESTION # 103
You have a Microsoft 365 E5 tenant.
You purchase a cloud app named App1.
You need to enable real-time session-level monitoring of App1 by using Microsoft Cloud app Security.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
1 - Publish App1 in Azure Active Directory (Azure AD).
2 - From Microsot Cloud App Security, modify...
3 - From Microsoft Cloud App Security, create...
4 - Create a conditional access policy...
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/proxy-deployment-any-app
https://docs.microsoft.com/en-us/cloud-app-security/session-policy-aad
NEW QUESTION # 104
You have an Azure Active Directory (Azure AD) tenant that contains three users named User1, User1, and User3, You create a group named Group1. You add User2 and User3 to Group1.
You configure a role in Azure AD Privileged identity Management (PIM) as shown in the application administrator exhibit. (Click the application Administrator tab.)
Group1 is configured as the approver for the application administrator role.
You configure User2to be eligible for the application administrator role.
For User1, you add an assignment to the Application administrator role as shown in the Assignment exhibit. (Click Assignment tab)
For each of the following statement, select Yes if the statement is true, Otherwise, select No.
NOTE: Each correct selection is worth one point.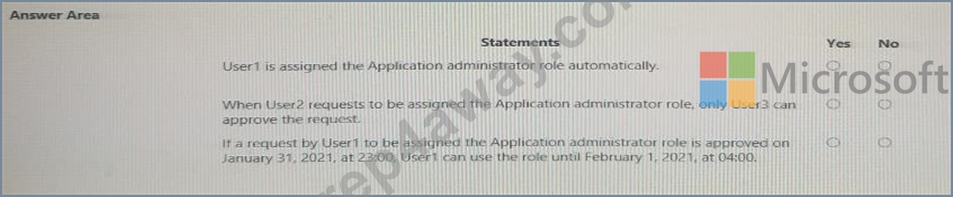
Answer:
Explanation:
NEW QUESTION # 105
Your company has an Azure Active Directory (Azure AD) tenant named contosri.com. The company has the business partners shown in the following table.
users can request access by using package 1.
Users at Fabrikam and Litware use ail then respective domain names for email addresses.
You plan to create an access package named packaqe1 that will be accessible only to the Fabrikam and Litware users.
You need to configure connected organizations for Fabrikam and litware so that any of their users can request access by using package1.
What is the minimum of connected organization that you should create.
- A. 0
- B. 1
- C. 2
- D. 3
Answer: D
NEW QUESTION # 106
You have a Microsoft Entra tenant that contains the users shown in the following table:
Admin4 creates a Conditional Access policy named Policy1 by using the "Require multifactor authentication for Azure management" template.
Which users will be required to use multi-factor authentication (MFA) the next time they sign in?
- A. Admin1, Admin2, Admin3, and Admin4
- B. Admin2 and Admin3 only
- C. Admin1 and Admin4 only
- D. Admin1, Admin2, and Admin3 only
Answer: C
Explanation:
Comprehensive and Detailed In-Depth Explanation:
Let's break this down step by step based on Microsoft Entra ID Conditional Access policies, the "Require multifactor authentication for Azure management" template, and the roles assigned to the users, as outlined in Microsoft Identity and Access Administrator documentation.
Understanding the "Require multifactor authentication for Azure management" Template:
Microsoft Entra ID Conditional Access policies allow administrators to enforce security controls, such as requiring multi-factor authentication (MFA), based on specific conditions.
The "Require multifactor authentication for Azure management" template is a predefined Conditional Access policy template in Microsoft Entra ID. This template is designed to secureaccess to Azure management interfaces, such as the Azure portal, Azure PowerShell, Azure CLI, and other Azure management endpoints.
Key Details of the Template:
Cloud Apps or Actions:The template targets the "Microsoft Azure Management" cloud app. This includes all Azure management interfaces but does not apply to other cloud apps (e.g., Microsoft 365 apps).
Users:By default, the template applies to "All users," but it can be modified to include or exclude specific users or groups. The question does not specify any modifications, so we assume the default "All users" scope.
Conditions:Typically, there are no specific conditions (e.g., device state, location) in this template unless modified.
Grant Controls:The template enforces "Require multi-factor authentication" as the access control.
Therefore, this policy will require MFA for any user who attempts to access Azure management interfaces.
Understanding the Roles and Their Interaction with Azure Management:
Let's examine the roles assigned to each user and whether they are likely to interact with Azure management interfaces:
Admin1: Global Administrator
A Global Administrator has full access to all Microsoft Entra ID and Azure resources, including the ability to manage Azure subscriptions, resources, and the Azure portal.
Global Administrators frequently access Azure management interfaces (e.g., the Azure portal) to perform administrative tasks. Therefore, Admin1 will be subject to the Conditional Access policy when they sign in to access Azure management.
Admin2: Conditional Access Administrator
A Conditional Access Administrator can manage Conditional Access policies in Microsoft Entra ID but does not have direct access to Azure management interfaces by default.
This role is focused on Microsoft Entra ID, not Azure resource management. Unless Admin2 has been granted additional Azure roles (e.g., Contributor, Owner), they are unlikely to access Azure management interfaces.
The question does not indicate any additional roles for Admin2, so we assume they do not interact with Azure management.
Admin3: Authentication Policy Administrator
An Authentication Policy Administrator can manage authentication methods and policies in Microsoft Entra ID (e.g., MFA settings, passwordless authentication).
Like the Conditional Access Administrator, this role is specific to Microsoft Entra ID and does not grant access to Azure management interfaces by default. Admin3 would not typically access Azure management unless assigned additional Azure roles, which are not specified.
Admin4: Global Administrator
Like Admin1, Admin4 is a Global Administrator and has full access to Azure management interfaces.
Admin4 will be subject to the Conditional Access policy when accessing Azure management.
Applying the Conditional Access Policy:
The policy applies to "All users" (default scope of the template) and targets the "Microsoft Azure Management" cloud app.
The policy requires MFA for any user who accesses Azure management interfaces.
Admin1 and Admin4 (Global Administrators):
As Global Administrators, both Admin1 and Admin4 will access Azure management interfaces (e.g., the Azure portal) as part of their administrative duties.
The next time they sign in to access Azure management, the Conditional Access policy (Policy1) will enforce MFA.
Admin2 (Conditional Access Administrator) and Admin3 (Authentication Policy Administrator):
These roles do not inherently grant access to Azure management interfaces. Their responsibilities are limited to Microsoft Entra ID tasks, such as managing Conditional Access policies or authentication methods.
Unless Admin2 or Admin3 attempts to access Azure management (which they are not authorized to do by default), the policy will not apply to them. The question asks about the "next time they sign in," but the policy only triggers MFA when accessing the targeted cloud app (Microsoft Azure Management). If Admin2 and Admin3 sign in to Microsoft Entra ID or other apps (e.g., Microsoft 365), the policy does not apply.
Analysis of the Options:
A). Admin2 and Admin3 only:
Incorrect. Admin2 and Admin3 are not likely to access Azure management interfaces based on their roles, so the policy will not require MFA for them.
B). Admin1 and Admin4 only:
Correct. Admin1 and Admin4 are Global Administrators who will access Azure management interfaces, triggering the policy to require MFA the next time they sign in to those interfaces.
C). Admin1, Admin2, and Admin3 only:
Incorrect. Admin2 and Admin3 are not subject to the policy for the reasons stated above.
D). Admin1, Admin2, Admin3, and Admin4:
Incorrect. While the policy applies to "All users," only Admin1 and Admin4 (Global Administrators) are likely to access Azure management interfaces, triggering the MFA requirement.
Additional Considerations:
If Admin2 or Admin3 were assigned additional Azure roles (e.g., Contributor, Owner) that grant access to Azure management, they would also be subject to the policy. However, the question does not indicate any such roles.
The phrase "the next time they sign in" can be misleading. The policy only enforces MFA when the user signs in to the targeted cloud app (Microsoft Azure Management). IfAdmin2 or Admin3 signs in to a different app (e.g., Microsoft 365), the policy does not apply.
If the policy were modified to target a different cloud app (e.g., "All apps") or to include specific users, the answer might change. However, the question specifies the default template behavior.
Conclusion:The Conditional Access policy (Policy1) created using the "Require multifactor authentication for Azure management" template will require MFA for users who access Azure management interfaces. Based on their roles:
Admin1 and Admin4 (Global Administrators) will be required to use MFA the next time they sign in to Azure management.
Admin2 and Admin3 (Conditional Access Administrator and Authentication Policy Administrator) are not likely to access Azure management, so the policy does not apply to them.Therefore, the correct answer isB.
References:
Microsoft Entra ID Conditional Access documentation: "Common Conditional Access policies - Require MFA for Azure management" (Microsoft Learn:https://learn.microsoft.com/en-us/entra/identity/conditional- access/concept-conditional-access-policy-common#require-mfa-for-azure-management) Microsoft Entra ID role documentation: "Administrator role permissions in Microsoft Entra ID" (Microsoft Learn:https://learn.microsoft.com/en-us/entra/identity/role-based-access-control/permissions-reference) Microsoft Identity and Access Administrator (SC-300) exam study guide, which covers Conditional Access policies and their application to specific roles and cloud apps.
NEW QUESTION # 107
Your company has two divisions named Contoso East and Contoso West. The Microsoft 365 identity architecture tor both divisions is shown in the following exhibit.
You need to assign users from the Contoso East division access to Microsoft SharePoint Online sites in the Contoso West tenant. The solution must not require additional Microsoft 3G5 licenses.
What should you do?
- A. Configure Azure AD Application Proxy in the Contoso West tenant.
- B. Invite the Contoso East users as guests in the Contoso West tenant.
- C. Deploy a second Azure AD Connect server to Contoso East and configure the server to sync the Contoso East Active Directory forest to the Contoso West tenant.
- D. Configure the exiting Azure AD Connect server in Contoso Cast to sync the Contoso East Active Directory forest to the Contoso West tenant.
Answer: B
Explanation:
In SC-300, Microsoft emphasizes Azure AD B2B collaboration for cross-tenant access without extra Microsoft 365 licensing. The guidance explains that organizations can invite external users as guests to their tenant to access Microsoft 365 resources such as SharePoint Online and Teams, and guest access does not require an additional Microsoft 365 license for the guest. The host tenant remains licensed for the workloads being accessed, and Azure AD billing for B2B collaboration is handled through External Identities (MAU) if configured. The study content also notes that synchronizing a single on-premises AD forest to multiple Azure AD tenants is not a supported topology with a single Azure AD Connect server, and deploying another AAD Connect to sync the same identities to a second tenant introduces complexity and is unnecessary when the requirement is simply to let users in one tenant access resources in another. Application Proxy (publishing on-prem apps) is unrelated to granting SharePoint Online cross-tenant access. Therefore, the minimum-effort, license-compliant approach is to invite Contoso East users as B2B guests in the Contoso West tenant and assign them the required SharePoint permissions.
NEW QUESTION # 108
You have an Azure Active Directory (Azure AD) tenant.
You configure self-service password reset (SSPR) by using the following settings:
- Require users to register when signing in: Yes
- Number of methods required to reset: 1
What is a valid authentication method available to users?
- A. a mobile app notification
- B. an email to an address in your organization
- C. an FIDO2 security token
- D. an email to an address outside your organization
Answer: D
Explanation:
When using a mobile app as a method for password reset, like the Microsoft Authenticator app, the following considerations apply:
- When administrators require one method be used to reset a password, verification code is the only option available.
- When administrators require two methods be used to reset a password, users are able to use notification OR verification code in addition to any other enabled methods.
https://learn.microsoft.com/en-us/azure/active-directory/authentication/concept-sspr- howitworks#mobile-app-and-sspr
NEW QUESTION # 109
You have a Microsoft 365 E5 subscription that contains a Microsoft SharePoint Online site named Site1 and the users shown in the following table.
The users have the devices shown in the following table.
You create the following two Conditional Access policies:
* Name: CAPolicy1
* Assignments
o Users or workload identities: Group 1
o Cloud apps or actions: Office 365 SharePoint Online
o Conditions
* Filter for devices: Exclude filtered devices from the policy
* Rule syntax: device.displayName -starts With "Device*"
o Access controls
* Grant: Block access
* Session: 0 controls selected
o Enable policy: On
* Name: CAPolicy2
* Assignments
o Users or workload identities: Group2
o Cloud apps or actions: Office 365 SharePoint Online
o Conditions: 0 conditions selected
* Access controls
o Grant: Grant access
* Require multifactor authentication
o Session:
0 controls selected
* Enable policy: On
All users confirm that they can successfully authenticate using MFA.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 110
You have a Microsoft Entra tenant that uses Microsoft Entra ID Premium licenses.
You plan to configure a terms of use (ToU) for the tenant.
You need to upload the ToU document.
Which format should you use for the document?
- A. PDF
- B. RTF
- C. DOCX
- D. HTML
Answer: A
Explanation:
The Microsoft Entra Terms of Use (ToU) documentation included in the SC-300 curriculum specifies that only PDF files are supported when uploading terms of use documents.
Microsoft Entra ID Premium licenses are required to configure Terms of Use, and when administrators create a new ToU, the upload field explicitly accepts a PDF document format. The PDF ensures consistent formatting across devices and preserves the legal structure of compliance statements.
The guide states:
"The terms of use document must be a PDF file. This ensures consistency in presentation and prevents tampering." Therefore, acceptable format: PDF only - formats such as HTML, DOCX, or RTF are not supported.
NEW QUESTION # 111
You have a Microsoft 365 tenant.
The Azure Active Directory (Azure AD) tenant syncs to an on-premises Active Directory domain. The domain contains the servers shown in the following table.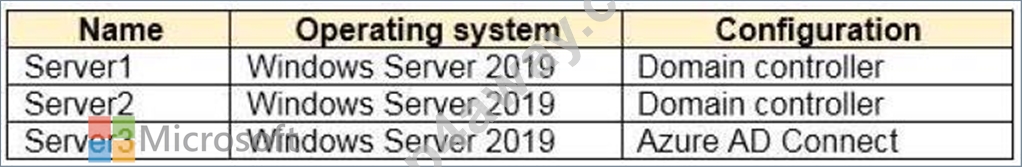
The domain controllers are prevented from communicating to the internet.
You implement Azure AD Password Protection on Server1 and Server2.
You deploy a new server named Server4 that runs Windows Server 2019.
You need to ensure that Azure AD Password Protection will continue to work if a single server fails.
What should you implement on Server4?
- A. the Azure AD Password Protection proxy service
- B. Azure AD Connect
- C. Azure AD Application Proxy
- D. Password Change Notification Service (PCNS)
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-password-ban-bad-on-premisesdep
NEW QUESTION # 112
Task 5
You need to assign a Windows 10/11 Enterprise E3 license to the Sg-Retail group.
Answer:
Explanation:
See the Explanation for the complete step by step solution
Explanation:
To assign a Windows 10/11 Enterprise E3 license to the Sg-Retail group, you can follow these steps:
Sign in to the Microsoft Entra admin center:
Make sure you have the role of Global Administrator or License Administrator.
Navigate to the licensing page:
Go to Billing > Licenses1.
Find the Windows 10/11 Enterprise E3 license:
Look for the Windows 10/11 Enterprise E3 license in the list of available products.
Assign licenses to the group:
Select the license and then choose Assign licenses.
Search for and select the Sg-Retail group.
Confirm the assignment and make sure that the correct number of licenses is available for the group.
Review and confirm the assignment:
Ensure that the licenses have been properly assigned to the Sg-Retail group without affecting other groups or users.
Monitor the license status:
Check the license usage and status to ensure that the Sg-Retail group members can utilize the Windows 10/11 Enterprise E3 features.
By following these steps, the Sg-Retail group should now have the Windows 10/11 Enterprise E3 licenses assigned to them.
NEW QUESTION # 113
SIMULATION
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:[email protected]
Microsoft 365 Password: =1122334455667788
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 99999999
You need to ensure that when users in the sg-Operations group go to the My Apps portal, a tab named Operations appears that contains only the following applications:
- LinkedIn
- Box
To complete this task, sign in to the appropriate admin center.
Answer:
Explanation: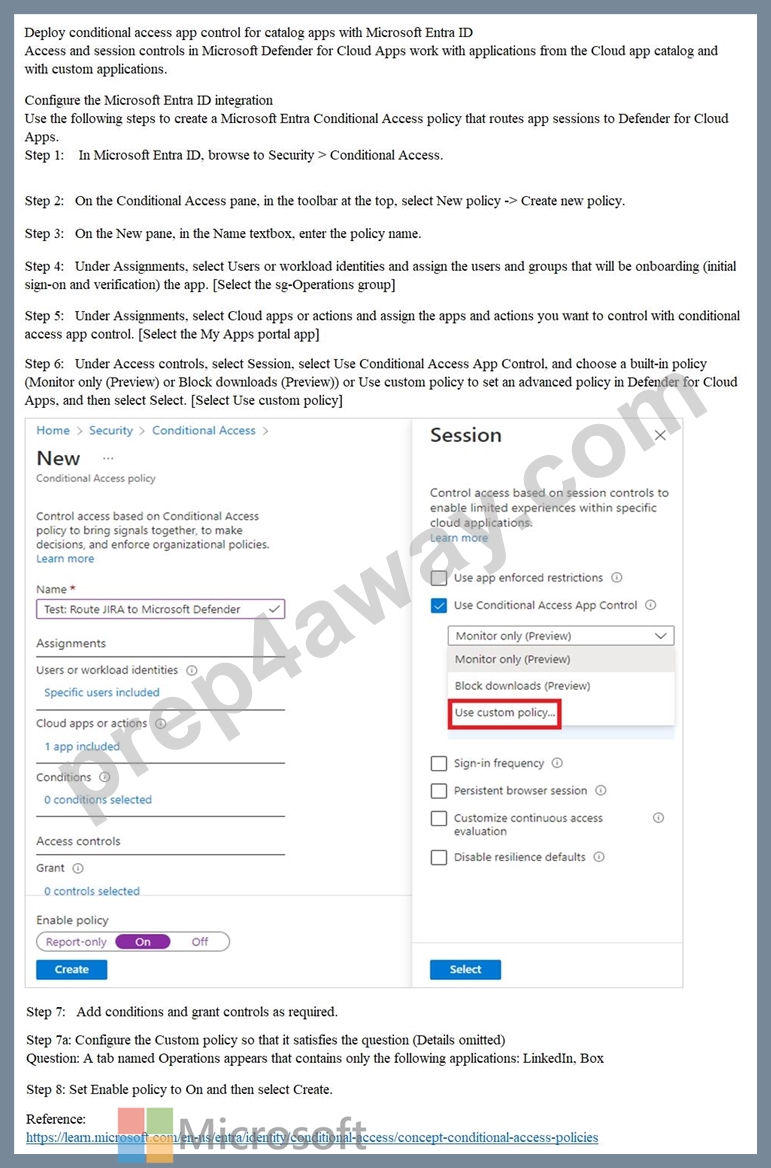
NEW QUESTION # 114
You have an Azure AD tenant contains the users shown in the following table.
In Azure AD Privileged Identity Management (PIM), you configure the Global Administrator role as shown in the following exhibit.
User 1 is eligible for the Global Administrator role.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 115
You have a Microsoft 365 tenant and an Active Directory domain named adatum.com.
You deploy Azure AD Connect by using the Express Settings.
You need to configure self-service password reset (SSPR) to meet the following requirements:
When users reset their password, they must be prompted to respond to a mobile app notification or answer three predefined security questions.
Passwords must be synced between the tenant and the domain regardless of where the password was reset.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.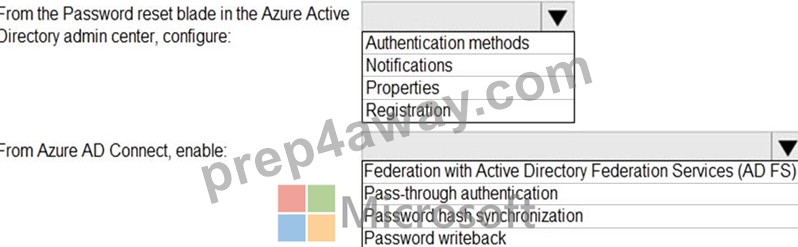
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-sspr-deployment
https://docs.microsoft.com/en-us/azure/active-directory/authentication/concept-authentication-security-questions
NEW QUESTION # 116
You need to configure the assignment of Azure AD licenses to the Litware users. The solution must meet the licensing requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 117
You have an Azure Active Directory (Azure AD) tenant that contains a user named User1 and the groups shown in the following table.
In the tenant, you create the groups shown in the following table.
Which members can you add to GroupA and GroupB? To answer, select the appropriate options in the answer area.
NOTE:Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Reference:
https://bitsizedbytes.wordpress.com/2018/12/10/distribution-security-and-office-365-groups-nesting/
NEW QUESTION # 118
You have a Microsoft 365 E5 subscription that contains two users named User1 and User2.
You need to ensure that User1 can create access reviews for groups, and that User2 can review the history report for all the completed access reviews. The solution must use the principle of least privilege.
Which role should you assign to each user? To answer, drag the appropriate roles to the correct users. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 119
You have a Microsoft Entra tenant that contains a terms of use (ToU) named Terms1. You create a Conditional Access policy named Policy1 to deploy Terms1. You need to configure Policy1 to require users to accept Terms1. Which settings should you configure for Policy1?
- A. Conditions
- B. Session
- C. Grant
- D. Target resources
Answer: C
Explanation:
Conditional Access policies evaluate Assignments (users, cloud apps), optional Conditions, and then enforce Access controls. In SC-300, Terms of use (ToU) is enforced via Grant controls: the policy must "require terms of use" so that users must accept a specified ToU before access is granted. The documentation states that the ToU experience is applied when a policy includes the control to "require terms of use," and this control lives under the Grant section (alongside controls like require MFA, require compliant device, etc.).
Therefore, to deploy Terms1 with Policy1, configure the Grant controls and select Require terms of use and choose Terms1. Conditions or Session settings do not trigger ToU acceptance; they refine when or how access is permitted. Target resources select apps, but the enforcement of acceptance is strictly a Grant control.
NEW QUESTION # 120
You need to implement password restrictions to meet the authentication requirements.
You install the Azure AD password Protection DC agent on DC1.
What should you do next? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Topic 3,
Overview
A Datum Environment
The on-premises network of A. Datum contains an Active Directory Domain Services (AD DS) forest named adatum.com.
The tenant contains the users shown in the following table.
Problem Statements
* Multiple users in the sales department have up to five devices. The sales department users report that sometimes they must contact the support department to join their devices to the Azure AD tenant because they have reached their device limit.
* A recent security incident reveals that several users leaked their credentials, a suspicious browser was used for a sign-in, and resources were accessed from an anonymous IP address,
* When you attempt to assign the Device Administrators role To IT_Group1, the group does NOT appear in the selection list.
* Anyone in the organization can invite guest users, including other guests and non-administrators.
* The helpdesk spends too much time resetting user passwords.
* Users currently use only passwords for authentication.
Requirements
A, Datum plans to implement the following changes;
* Configure self-service password reset {SSPR}.
* Configure multi-factor authentication (MFA) for all users.
* Configure an access review for an access package named Package1.
* Require admin approval for application access to organizational data.
* Sync the AD DS users and groupsoflitware.com with the Azure AD tenant.
* Ensure that only users that are assigned specific admin roles can invite guest users.
* Increase the maximum number of devices that can be joined or registered to Azure AD to 10.
Technical Requirements
* Users assigned the User administrator role must be able to request permission to use the role when needed for up to one year.
* Users must be prompted to register for MFA and provided with an option to bypass the registration for a grace period.
* Users must provide one authentication method to reset their password by using SSPR. Available methods must include:
* Email
* Phone
* Security questions
* The Microsoft Authenticator app
* Trust relationships must NOT be established between the adatum.com and litware.com AD DS domains.
* The principle of least privilege must be used.
NEW QUESTION # 121
You have an Azure AD tenant that contains the users shown in the following table.
In Azure AD Identity Protection, you configure a user risk policy that has the following settings:
* Assignments:
o Users: Group1
o User risk: Low and above
* Controls:
o Access: Block access
* Enforce policy: On
In Azure AD Identity Protection, you configure a sign-in risk policy that has the following settings:
* Assignments:
o Users: Group2
o Sign-in risk: Low and above
* Controls:
o Access: Require multi-factor authentication
* Enforce policy. On
the following settings:
ng settings:
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 122
You have a Microsoft Entra tenant named contoso.com that contains an enterprise application named App1.
A contractor uses the credentials of [email protected].
You need to ensure that you can provide the contractor with access to App1. The contractor must be able to authenticate as [email protected].
What should you do?
- A. Create a guest user account in contoso.com.
- B. Configure the External collaboration settings.
- C. Implement Microsoft Entra Connect sync.
- D. Run the New-MgUser cmdlet.
Answer: A
NEW QUESTION # 123
You have a Microsoft 36S tenant.
You create a named location named HighRiskCountries that contains a list of high-risk countries.
You need to limit the amount of time a user can stay authenticated when connecting from a high-risk country.
What should you configure in a conditional access policy? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 124
You have an Azure subscription that contains the resources shown in the following table.
You need to configure access to Vault1. The solution must meet the following requirements:
* Ensure that User1 can manage and create keys in Vault1.
* Ensure that User2 can access a certificate stored in Vault1.
* Use the principle of least privilege.
Which role should you assign to each user? To answer select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 125
......
Microsoft SC-300 exam is ideal for IT professionals who work with identity and access solutions in Microsoft 365 and Azure environments. Microsoft Identity and Access Administrator certification is a great way to demonstrate your expertise in these areas, and it can help you advance your career. SC-300 exam is also an excellent opportunity to gain knowledge and skills that are in high demand in the IT industry. As the demand for cloud-based identity and access management solutions continues to grow, the Microsoft SC-300 certification can give you a competitive edge in the job market.
Actual Questions Answers Pass With Real SC-300 Exam Dumps: https://www.prep4away.com/Microsoft-certification/braindumps.SC-300.ete.file.html
Pass Your Exam Easily! SC-300 Real Question Answers Updated: https://drive.google.com/open?id=1CO7EOzUSfvgXb9yhEsDV6hJN9wgJIg1Y