

Real CompTIA CS0-002 Exam Questions [Updated 2025]
CS0-002 Exam Dumps Pass with Updated 2025 CompTIA Cybersecurity Analyst (CySA+) Certification Exam
CompTIA CS0-002 exam is designed to validate the skills and knowledge of cybersecurity analysts in detecting and responding to cybersecurity threats. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification is ideal for professionals who work in the field of cybersecurity and want to advance their career. CS0-002 exam covers various topics such as threat management, vulnerability management, incident response, and compliance and assessment. By passing CS0-002 exam, candidates can demonstrate their ability to protect organizations from cyber attacks, identify and analyze threats, and develop effective security solutions.
NEW QUESTION # 133
A new on-premises application server was recently installed on the network. Remote access to the server was enabled for vendor support on required ports, but recent security reports show large amounts of data are being sent to various unauthorized networks through those ports.
Which of the following configuration changes must be implemented to resolve this security issue while still allowing remote vendor access?
- A. Enable port security.
- B. Block the unauthorized networks.
- C. Sandbox the application server.
- D. Whitelist the application server.
- E. Apply a firewall application server rule.
Answer: D
NEW QUESTION # 134
A security analyst scanned an internal company subnet and discovered a host with the following Nmap output.
Based on the output of this Nmap scan, which of the following should the analyst investigate FIRST?
- A. Port 135
- B. Port 22
- C. Port 3389
- D. Port 445
Answer: A
NEW QUESTION # 135
A security analyst is reviewing the following log from an email security service.
Which of the following BEST describes the reason why the email was blocked?
- A. The email originated from the www.spamfilter.org URL.
- B. The IP address and the remote server name are the same.
- C. The IP address was blacklisted.
- D. The To address is invalid.
- E. The From address is invalid.
Answer: C
NEW QUESTION # 136
A user's computer has been running slowly when the user tries to access web pages. A security analyst runs the command netstat -aon from the command line and receives the following output:
Which of the following lines indicates the computer may be compromised?
- A. Line 1
- B. Line 4
- C. Line 5
- D. Line 6
- E. Line 2
- F. Line 3
Answer: B
NEW QUESTION # 137
A company installed a wireless network more than a year ago, standardizing on the same model APs in a single subnet. Recently, several users have reported timeouts and connection issues with Internet browsing. The security administrator has gathered some information about the network to try to recreate the issues with the assistance of a user. The administrator is able to ping every device on the network and confirms that the network is very slow.
Output: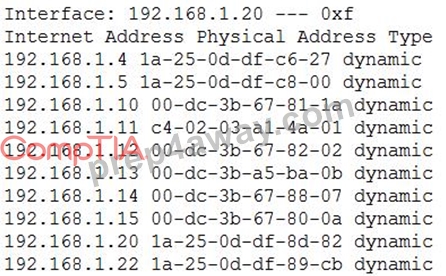
Given the above results, which of the following should the administrator investigate FIRST?
- A. The device at 192.168.1.4
- B. The AP-IT device
- C. The AP-Workshop device
- D. The user's PC
- E. The AP-Reception device
Answer: C
NEW QUESTION # 138
A security analyst is reviewing the following log from an email security service.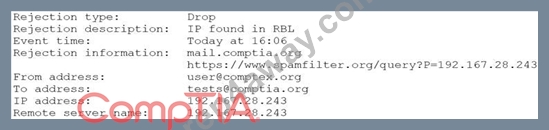
Which of the following BEST describes the reason why the email was blocked?
- A. The email originated from the www.spamfilter.org URL.
- B. The IP address and the remote server name are the same.
- C. The IP address was blacklisted.
- D. The To address is invalid.
- E. The From address is invalid.
Answer: C
NEW QUESTION # 139
An information security analyst discovered a virtual machine server was compromised by an attacker. Which of the following should be the FIRST step to confirm and respond to the incident?
- A. Remove the NIC from the virtual machine.
- B. Pause the virtual machine.
- C. Take a snapshot of the virtual machine.
- D. Shut down the virtual machine.
Answer: B
Explanation:
Explanation
Enumeration is the process of discovering and listing information. Network enumeration is the process of discovering pieces of information that might be helpful in a network attack or compromise. There are several techniques used to perform enumeration and several tools that make the process easier for both testers and attackers. Let's take a look at these techniques and tools.
NEW QUESTION # 140
A security analyst wants to identify which vulnerabilities a potential attacker might initially exploit if the network is compromised. Which of the following would provide the BEST results?
- A. External penetration test
- B. Network ping sweep
- C. Baseline configuration assessment
- D. Uncredentialed scan
Answer: D
NEW QUESTION # 141
A security analyst at exampte.com receives a SIEM alert for an IDS signature and reviews the associated packet capture and TCP stream:

Winch of the following actions should the security analyst lake NEXT?
- A. Raise a request to the firewall team to block 203.0.113.15.
- B. Contact the application owner for connect example local tor additional information
- C. Mark the alert as a false positive scan coming from an approved source.
- D. Review the known Apache vulnerabilities to determine if a compromise actually occurred
Answer: A
NEW QUESTION # 142
A cybersecurity analyst has access to several threat feeds and wants to organize them while simultaneously comparing intelligence against network traffic.
Which of the following would BEST accomplish this goal?
- A. Information sharing and analysis
- B. Continuous integration and deployment
- C. Automation and orchestration
- D. Static and dynamic analysis
Answer: D
NEW QUESTION # 143
A small electronics company decides to use a contractor to assist with the development of a new FPGA-based device. Several of the development phases will occur off-site at the contractor's labs.
Which of the following is the main concern a security analyst should have with this arrangement?
- A. Moving the FPGAs between development sites will lessen the time that is available for security testing.
- B. Development phases occurring at multiple sites may produce change management issues.
- C. Making multiple trips between development sites increases the chance of physical damage to the FPGAs.
- D. FPGA applications are easily cloned, increasing the possibility of intellectual property theft.
Answer: D
Explanation:
Explanation/Reference: https://www.eetimes.com/how-to-protect-intellectual-property-in-fpgas-devices-part-1/#
NEW QUESTION # 144
A security technician is testing a solution that will prevent outside entities from spoofing the company's email domain, which is comptiA.org. The testing is successful, and the security technician is prepared to fully implement the solution.
Which of the following actions should the technician take to accomplish this task?
- A. Add TXT @ "v=spf1 mx include:_spf.comptiA.org all" to the email server.
- B. Add TXT @ "v=spf1 mx include:_spf.comptiA.org +all" to the domain controller.
- C. Add TXT @ "v=spf1 mx include:_spf.comptiA.org all" to the DNS record.
- D. Add TXT @ "v=spf1 mx include:_spf.comptiA.org +all" to the web server.
Answer: C
Explanation:
Reference: https://blog.finjan.com/email-spoofing/
NEW QUESTION # 145
A security analyst needs to provide the development team with secure connectivity from the corporate network to a three-tier cloud environment. The developers require access to servers in all three tiers in order to perform various configuration tasks. Which of the following technologies should the analyst implement to provide secure transport?
- A. VPN
- B. CASB
- C. VPC
- D. Federation
Answer: A
NEW QUESTION # 146
The steering committee for information security management annually reviews the security incident register for the organization to look for trends and systematic issues The steering committee wants to rank the risks based on past incidents to improve the security program for next year Below is the incident register for the organization.
Which of the following should the organization consider investing in FIRST due to the potential impact of availability?
- A. Hire additional staff for the IT department to assist with vulnerability management and log review
- B. Hire a managed service provider to help with vulnerability management
- C. Invest in a failover and redundant system, as necessary
- D. Build a warm site in case of system outages
Answer: C
Explanation:
Both on July 31 and November 24, the organization could not restore multiple days due to missing disaster recovery plan. Therefore, failover systems are very important for this organization.
NEW QUESTION # 147
An analyst performs a routine scan of a host using Nmap and receives the following output:
Which of the following should the analyst investigate FIRST?
- A. Port 80
- B. Port 21
- C. Port 23
- D. Port 22
Answer: B
NEW QUESTION # 148
A security analyst performed a review of an organization's software development life cycle. The analyst reports that the life cycle does not contain in a phase in which team members evaluate and provide critical feedback on another developer's code. Which of the following assessment techniques is BEST for describing the analyst's report?
- A. Whitebox testing
- B. Architectural evaluation
- C. Waterfall
- D. Peer review
Answer: D
NEW QUESTION # 149
Given the following code:
Which of the following types of attacks is occurring in the example above?
- A. XSS
- B. SQL injection
- C. Session hijacking
- D. Privilege escalation
- E. MITM
Answer: B
NEW QUESTION # 150
A security analyst implemented a solution that would analyze the attacks that the organization's firewalls failed to prevent. The analyst used the existing systems to enact the solution and executed the following command.
S sudo nc -1 -v -c maildemon . py 25 caplog, txt
Which of the following solutions did the analyst implement?
- A. Log collector
- B. Honeypot
- C. Snikhole
- D. Crontab mail script
Answer: A
NEW QUESTION # 151
A Chief Executive Officer (CEO) is concerned about the company's intellectual property being leaked to competitors. The security team performed an extensive review but did not find any indication of an outside breach. The data sets are currently encrypted using the Triple Data Encryption Algorithm. Which of the following courses of action is appropriate?
- A. Use data tokenization on sensitive fields, reencrypt the data sets using AES-256, and then create an MD5 hash.
- B. Ensure the data is correctly classified and labeled, and that DLP rules are appropriate to prevent disclosure.
- C. Limit all access to the sensitive data based on geographic access requirements with strict role-based access controls.
- D. Enable data masking and reencrypt the data sets using AES-256.
Answer: D
Explanation:
Data masking is a technique that replaces sensitive data with fictitious but realistic data, thus preventing unauthorized access to the original data. Reencrypting the data sets using AES-256 would provide a stronger level of encryption than Triple DES, which has been deprecated by NIST due to its vulnerability to attacks12
NEW QUESTION # 152
A SIEM alert occurs with the following output:
Which of the following BEST describes this alert?
- A. The alert is valid because IP spoofing may be occurring on the network
- B. The alert is valid because there may be a rogue device on the network
- C. The alert is a false positive; both NICs are of the same brand
- D. The alert is a false positive; there is a device with dual NICs
Answer: A
NEW QUESTION # 153
A security analyst is investigating a malware infection that occurred on a Windows system. The system was not connected to a network and had no wireless capability Company policy prohibits using portable media or mobile storage The security analyst is trying to determine which user caused the malware to get onto the system Which of the following registry keys would MOST likely have this information?
- A. HKEY_USERS\<user SID>\Software\Microsoft\Windows\explorer\MountPoints2
- B. HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\services\eventlog\System\iusb3hub
- C. HKEY_USERS\<user SID>\Software\Microsoft\Windows\CurrentVersion\Run
- D. HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run
- E. HKEY_USERS\<user SID>\Software\Microsoft\Internet Explorer\Typed URLs
Answer: B
NEW QUESTION # 154
Considering confidentiality and integrity, which of the following make servers more secure than desktops? (Select THREE).
- A. Hard drive capacity
- B. VLANs
- C. Physical access restriction
- D. Trained operators
- E. Processing power
- F. OS
Answer: C,D,F
NEW QUESTION # 155
......
CompTIA Cybersecurity Analyst (CySA+) certification exam or CS0-002, is an advanced-level certification that validates the skills and knowledge of IT professionals in the field of cybersecurity. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification exam is designed to assess the skills required to identify, prevent, and respond to cybersecurity threats and vulnerabilities. CS0-002 exam covers a wide range of topics, including threat and vulnerability management, incident response, security architecture and toolsets, and compliance and regulations.
CS0-002 Exam Dumps, CS0-002 Practice Test Questions: https://www.prep4away.com/CompTIA-certification/braindumps.CS0-002.ete.file.html
Free CS0-002 Exam Dumps to Pass Exam Easily: https://drive.google.com/open?id=1pbTx6HYpylwqlWUw81dbgyBsIpaXh9x_