

[Aug-2022] Free PCNSE Exam Dumps to Improve Exam Score
2022 Realistic PCNSE Dumps Exam Tips Test Pdf Exam Material
NEW QUESTION 48
A Palo Alto Networks firewall is being targeted by an NTP Amplification attack and is being flooded with tens thousands of bogus UDP connections per second to a single destination IP address and post.
Which option when enabled with the correction threshold would mitigate this attack without dropping legitirnate traffic to other hosts insides the network?
- A. QoS Policy to throttle traffic below maximum limit
- B. Security Policy rule to deny trafic to the IP address and port that is under attack
- C. Classified DoS Protection Policy using destination IP only with a Protect action
- D. Zone Protection Policy with UDP Flood Protection
Answer: C
NEW QUESTION 49
An administrator is using Panorama and multiple Palo Alto Networks NGFWs. After upgrading all devices to the latest PAN-OS software, the administrator enables log forwarding from the firewalls to PanoramA.
Pre-existing logs from the firewalls are not appearing in PanoramA.
Which action would enable the firewalls to send their pre-existing logs to Panorama?
- A. Use the ACC to consolidate pre-existing logs.
- B. The log database will need to exported form the firewalls and manually imported into Panorama.
- C. Use the import option to pull logs into Panorama.
- D. A CLI command will forward the pre-existing logs to Panorama.
Answer: D
Explanation:
Explanation
https://docs.paloaltonetworks.com/pan-os/8-0/pan-os-new-features/management-features/pa-7000-series-firewall
https://docs.paloaltonetworks.com/panorama/9-0/panorama-admin/set-up-panorama/install-content-and-software
NEW QUESTION 50
An administrator has configured the Palo Alto Networks NGFW's management interface to connect to the internet through a dedicated path that does not traverse back through the NGFW itself.
Which configuration setting or step will allow the firewall to get automatic application signature updates?
- A. A Security policy rule will need to be configured to allow the update requests from the firewall to the update servers.
- B. A service route will need to be configured.
- C. A Threat Prevention license will need to be installed.
- D. A scheduler will need to be configured for application signatures.
Answer: B
Explanation:
Explanation/Reference:
Explanation:
The firewall uses the service route to connect to the Update Server and checks for new content release versions and, if there are updates available, displays them at the top of the list.
Reference: https://www.paloaltonetworks.com/documentation/80/pan-os/web-interface-help/device/device- dynamic-updates
NEW QUESTION 51
Refer to Exhibit:

A firewall has three PDF rules and a default route with a next hop of 172.29.19.1 that is configured in the default VR. A user named XX-bes a PC with a 192.168.101.10 IP address.
He makes an HTTPS connection to 172.16.10.29.
What is the next hop IP address for the HTTPS traffic from Wills PC.
- A. 172.20.20.1
- B. 172.20.40.1
- C. 172.20.30.1
- D. 172.20.10.1
Answer: A
NEW QUESTION 52
An administrator needs to determine why users on the trust zone cannot reach certain websites. The only information available is shown on the following image. Which configuration change should the administrator make?
A)
B)
C)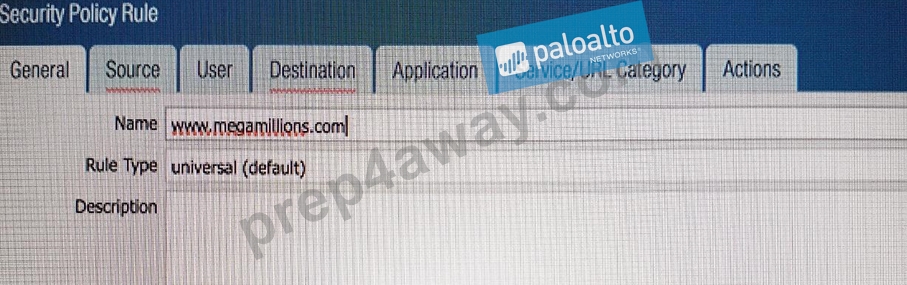
D)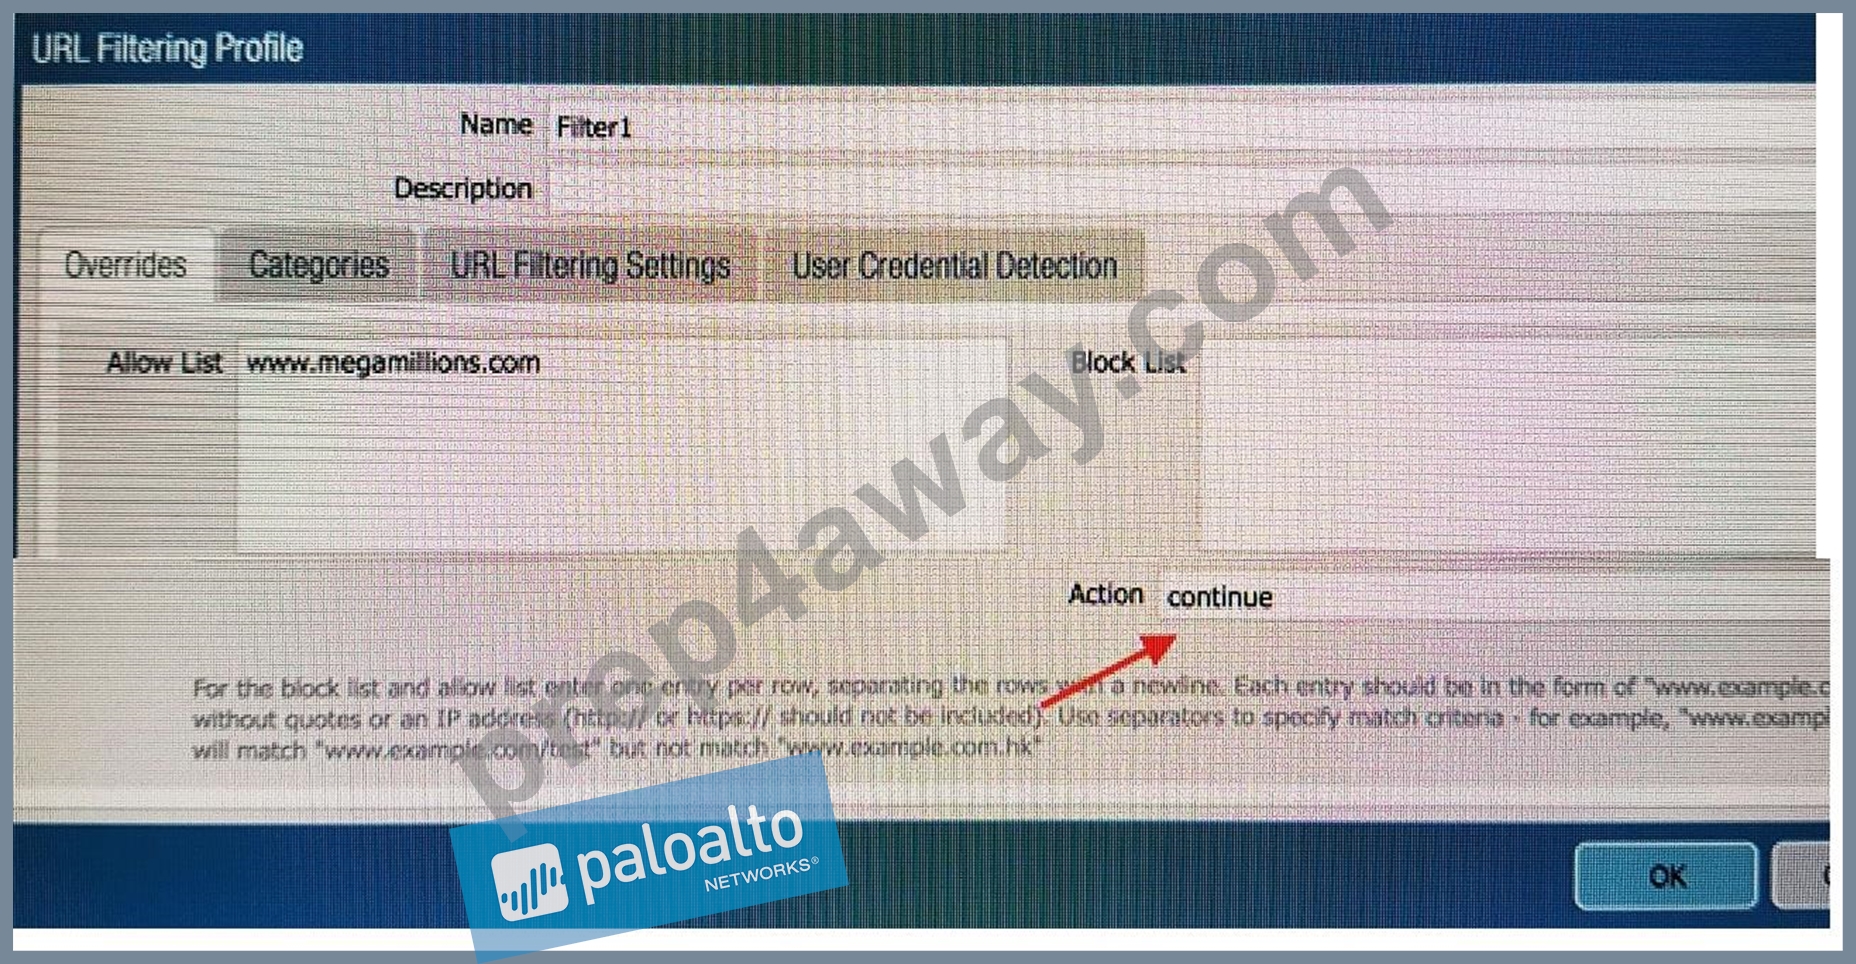
E)
- A. Option A
- B. Option E
- C. Option B
- D. Option D
- E. Option C
Answer: D
NEW QUESTION 53
An engineer is pushing configuration from Panorama lo a managed firewall.
What happens when the pushed Panorama configuration has Address Object names that duplicate the Address Objects already configured on the firewall?
- A. The firewall ignores only the pushed objects that have the same name as the locally configured objects, and it will commit the rest of the pushed configuration.
- B. The firewall fully commits all of the pushed configuration and overwrites its locally configured objects
- C. The firewall renames the duplicate local objects with "-1" at the end signifying they are clones; it will update the references to the objects accordingly and fully commit the pushed configuration.
- D. The firewall rejects the pushed configuration, and the commit fails.
Answer: D
NEW QUESTION 54
SAML SLO is supported for which two firewall features? (Choose two.)
- A. GlobalProtect Portal
- B. CLI
- C. WebUI
- D. CaptivePortal
Answer: A,C
Explanation:
SSO is available to administrators who access the web interface and to end users who access applications through GlobalProtect or Captive Portal. SLO is available to administrators and GlobalProtect end users, but not to Captive Portal end users. https://docs.paloaltonetworks.com/pan-os/9-0/pan-os-admin/authentication/authentication-types/saml
https://docs.paloaltonetworks.com/pan-os/10-0/pan-os-web-interface-help/device/device-server-profiles-saml-identity-provider
NEW QUESTION 55
Which of the following commands would you use to check the total number of the sessions that are currently going through SSL Decryption processing?
- A. show session all ssI-decrypt yes count yes
- B. show session filter ssl-decryption yes total-count yes
- C. show session all filter ssl-decrypt yes count yes
- D. show session all filter ssl-decryption yes total-count yes
Answer: C
NEW QUESTION 56
Which virtual router feature determines if a specific destination IP address is reachable?
- A. Heartbeat Monitoring
- B. Failover
- C. Ping-Path
- D. Path Monitoring
Answer: D
Explanation:
Reference: https://www.paloaltonetworks.com/documentation/71/pan-os/pan-os/policy/pbf
NEW QUESTION 57
A network Administrator needs to view the default action for a specific spyware signature. The administrator follows the tabs and menus through Objects> Security Profiles> Anti-Spyware and select default profile.
What should be done next?
- A. View the default actions displayed in the Action column.
- B. Click the Rules tab and then look for rules with "default" in the Action column.
- C. Click the Exceptions tab and then click show all signatures.
- D. Click the simple-critical rule and then click the Action drop-down list.
Answer: C
NEW QUESTION 58
Which method does an administrator use to integrate all non-native MFA platforms in PAN-OS software?
- A. Okta
- B. PingID
- C. RADIUS
- D. DUO
Answer: C
Explanation:
Explanation
https://docs.paloaltonetworks.com/pan-os/8-1/pan-os-admin/authentication/authentication-types/multi-factor-auth For end-user authentication via Authentication Policy, the firewall directly integrates with several MFA platforms (Duo v2, Okta Adaptive, PingID, and RSA SecurID), as well as integrating through RADIUS or SAML for all other MFA platforms.
NEW QUESTION 59
An engineer has been tasked with reviewing traffic logs to find applications the firewall is unable to identify with App-ID. Why would the application field display as incomplete?
- A. The TCP connection did not fully establish.
- B. There is insufficient application data after the TCP connection was established.
- C. The TCP connection was terminated without identifying any application data.
- D. The client sent a TCP segment with the PUSH flag set.
Answer: B
NEW QUESTION 60
A company needs to preconfigure firewalls to be sent to remote sites with the least amount of preconfiguration.
Once deployed each firewall must establish secure tunnels back to multiple regional data centers to include the future regional data centers.
Which VPN preconfigured configuration would adapt to changes when deployed to the future site?
- A. GlobalProtect client
- B. GlobalProtect satellite
- C. IPsec tunnels using IKEv2
- D. PPTP tunnels
Answer: B
Explanation:
https://docs.paloaltonetworks.com/pan-os/10-1/pan-os-web-interface-help/globalprotect/network- globalprotect-portals/globalprotect-portals-satellite-configuration-tab.html
NEW QUESTION 61
What type of address object would be useful for internal devices where the addressing structure assigns meaning to certain bits in the address, as illustrated in the diagram?
- A. IP Range
- B. IP Wildcard Mask
- C. IP Address
- D. IP Netmask
Answer: B
NEW QUESTION 62
When planning to configure SSL Froward Proxy on a PA 5260, a user asks how SSL decryption can be implemented using phased approach in alignment with Palo Alto Networks best practices What should you recommend?
- A. Enable SSL decryption for known malicious destination IP addresses
- B. Enable SSL decryption for source users and known malicious URL categories
- C. Enable SSL decryption for known malicious source IP addresses
- D. Enable SSL decryption for malicious source users
Answer: A
NEW QUESTION 63
Which command can be used to validate a Captive Portal policy?
- A. test authentication-policy-match <criteria>
- B. request cp-policy-eval <criteria>
- C. debug cp-policy <criteria>
- D. eval captive-portal policy <criteria>
Answer: A
Explanation:
https://docs.paloaltonetworks.com/pan-os/8-0/pan-os-cli-quick-start/use-the-cli/test-the- configuration/test-policy-matches
NEW QUESTION 64
......
It is also recommended that the students explore other prep resources available at the Palo Alto Networks education website. The recommended tools include:
- Cybersecurity Skills Practice Lab
- Palo Alto PCNSE Study Guide & Practice Exam
- Preparation videos & tutorials
- Administrator’s guide
Powerful PCNSE PDF Dumps for PCNSE Questions: https://www.prep4away.com/Palo-Alto-Networks-certification/braindumps.PCNSE.ete.file.html
Authentic PCNSE Dumps - Free PDF Questions to Pass: https://drive.google.com/open?id=1m56Jss3TXkThwqb3QNZYc9KkJ7QFsCH9