

[Full-Version] 2024 New PCNSE Actual Exam Dumps, Palo Alto Networks Practice Test
Study HIGH Quality PCNSE Free Study Guides and Exams Tutorials
NEW QUESTION # 107
Which protection feature is available only in a Zone Protection Profile?
- A. ICMP Flood Protection
- B. SYN Flood Protection using SYN Flood Cookies
- C. Port Scan Protection
- D. UDP Flood Protections
Answer: B
Explanation:
Explanation
https://docs.paloaltonetworks.com/pan-os/7-1/pan-os-web-interface-help/network/network-network-profiles-zone
NEW QUESTION # 108
An administrator needs to determine why users on the trust zone cannot reach certain websites. The only information available is shown on the following image. Which configuration change should the administrator make?
A)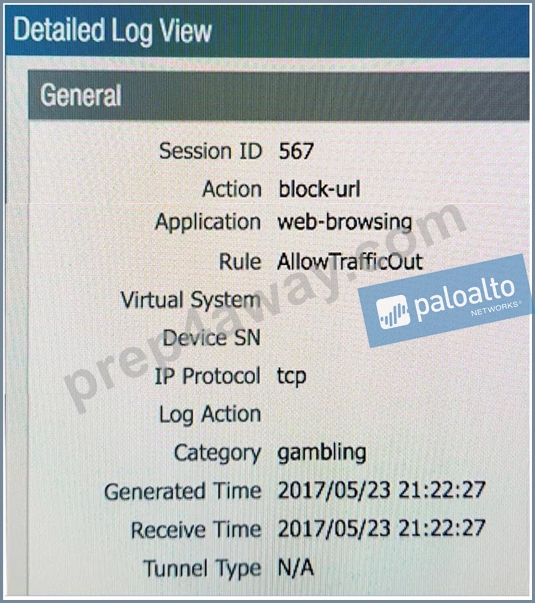
B)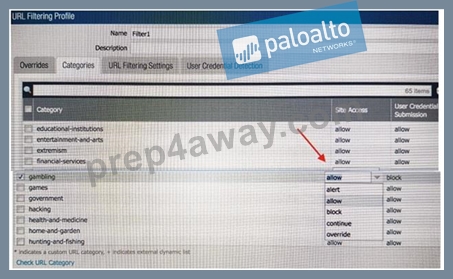
C)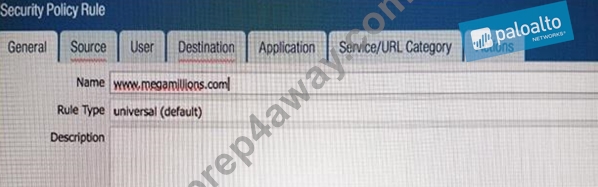
D)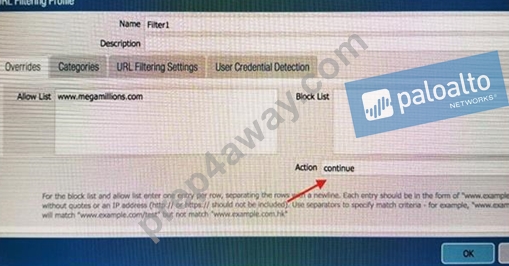
E)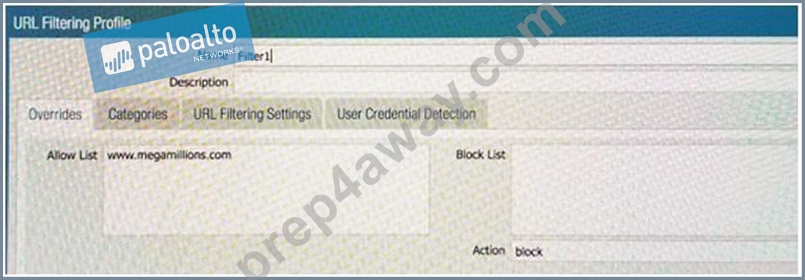
- A. Option C
- B. Option E
- C. Option A
- D. Option B
- E. Option D
Answer: E
NEW QUESTION # 109
Refer to the exhibit.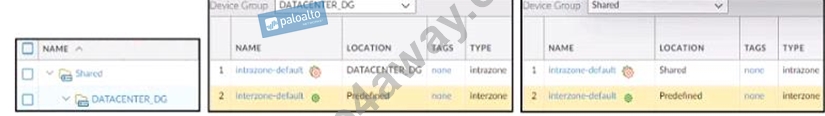
Based on the screenshots above what is the correct order in which the various rules are deployed to firewalls inside the DATACENTER_DG device group?
- A. shared pre-rules
DATACENTER DG pre rules
rules configured locally on the firewall
shared post-rules
DATACENTER_DG post-rules
DATACENTER.DG default rules - B. shared pre-rules
DATACENTER_DG pre-rules
rules configured locally on the firewall
shared post-rules
DATACENTER.DG post-rules
shared default rules - C. shared pre-rules
DATACENTER_DG pre-rules
rules configured locally on the firewall
DATACENTER_DG post-rules
shared post-rules
shared default rules - D. shared pre-rules
DATACENTER_DG pre-rules
rules configured locally on the firewall
DATACENTER_DG post-rules
shared post-rules
DATACENTER_DG default rules
Answer: A
NEW QUESTION # 110
Which option is part of the content inspection process?
- A. IPsec tunnel encryption
- B. Packet egress process
- C. Packet forwarding process
- D. SSL Proxy re-encrypt
Answer: D
NEW QUESTION # 111
Which configuration is backed up using the Scheduled Config Export feature in Panorama?
- A. Panorama candidate configuration
- B. Panorama running configuration and running configuration of all managed devices
- C. Panorama running configuration
- D. Panorama candidate configuration and candidate configuration of all managed devices
Answer: B
NEW QUESTION # 112
An organization wants to begin decrypting guest and BYOD traffic.
Which NGFW feature can be used to identify guests and BYOD users, instruct them how to download and install the CA certificate, and clearly notify them that their traffic will be decrypted?
- A. SSL decryption policy
- B. Authentication Portal
- C. comfort pages
- D. SSL Decryption profile
Answer: B
Explanation:
An authentication portal is a feature that can be used to identify guests and BYOD users, instruct them how to download and install the CA certificate, and clearly notify them that their traffic will be decrypted. An authentication portal is a web page that the firewall displays to users who need to authenticate before accessing the network or the internet. The authentication portal can be customized to include a welcome message, a login prompt, a disclaimer, a certificate download link, and a logout button. The authentication portal can also be configured to use different authentication methods, such as local database, RADIUS, LDAP, Kerberos, or SAML1. By using an authentication portal, the firewall can redirect BYOD users to a web page where they can learn about the decryption policy, download and install the CA certificate, and agree to the terms of use before accessing the network or the internet2.
An SSL decryption profile is not a feature that can be used to identify guests and BYOD users, instruct them how to download and install the CA certificate, and clearly notify them that their traffic will be decrypted. An SSL decryption profile is a set of options that define how the firewall handles SSL/TLS traffic that it decrypts. An SSL decryption profile can include settings such as certificate verification, unsupported protocol handling, session caching, session resumption, algorithm selection, etc3. An SSL decryption profile does not provide any user identification or notification functions.
An SSL decryption policy is not a feature that can be used to identify guests and BYOD users, instruct them how to download and install the CA certificate, and clearly notify them that their traffic will be decrypted. An SSL decryption policy is a set of rules that determine which traffic the firewall decrypts based on various criteria, such as source and destination zones, addresses, users, applications, services, etc. An SSL decryption policy can also specify which type of decryption to apply to the traffic, such as SSL Forward Proxy, SSL Inbound Inspection, or SSH Proxy4. An SSL decryption policy does not provide any user identification or notification functions.
Comfort pages are not a feature that can be used to identify guests and BYOD users, instruct them how to download and install the CA certificate, and clearly notify them that their traffic will be decrypted. Comfort pages are web pages that the firewall displays to users when it blocks or fails to decrypt certain traffic due to security policy or technical reasons. Comfort pages can include information such as the reason for blocking or failing to decrypt the traffic, the URL of the original site, the firewall serial number, etc5. Comfort pages do not provide any user identification or notification functions before decrypting the traffic.
Reference: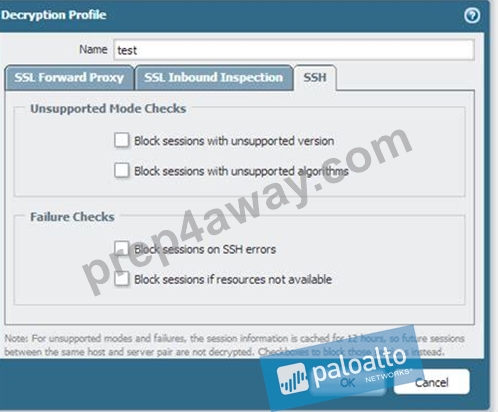
NEW QUESTION # 113
A session in the Traffic log is reporting the application as "incomplete." What does "incomplete" mean?
- A. The three-way TCP handshake was observed, but the application could not be identified.
- B. The three-way TCP handshake did not complete.
- C. The traffic is coming across UDP, and the application could not be identified.
- D. Data was received but was instantly discarded because of a Deny policy was applied before App-ID could be applied.
Answer: C
NEW QUESTION # 114
A network administrator wants to use a certificate for the SSL/TLS Service Profile.
Which type of certificate should the administrator use?
- A. certificate authority (CA) certificate
- B. server certificate
- C. client certificate
- D. machine certificate
Answer: B
Explanation:
Explanation
Use only signed certificates, not CA certificates, in SSL/TLS service profiles.
https://docs.paloaltonetworks.com/pan-os/10-1/pan-os-admin/certificate-management/configure-an-ssltls-service
NEW QUESTION # 115
Which PAN-OS® policy must you configure to force a user to provide additional credentials before he is allowed to access an internal application that contains highly-sensitive business data?
- A. Application Override policy
- B. Decryption policy
- C. Authentication policy
- D. Security policy
Answer: C
Explanation:
Authentication policy enables you to authenticate end users before they can access services and applications. Whenever a user requests a service or application (such as by visiting a web page), the firewall evaluates Authentication policy. Based on the matching Authentication policy rule, the firewall then prompts the user to authenticate using one or more methods (factors), such as login and password, Voice, SMS, Push, or One-time Password (OTP) authentication
https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-admin/authentication/authentication-policy
NEW QUESTION # 116
You have upgraded Panorama to 10.2 and need to upgrade six Log Collectors.
When upgrading Log Collectors to 10.2, you must do what?
- A. Add a Global Authentication Profile to each Managed Collector.
- B. Upgrade the Log Collectors one at a time.
- C. Upgrade all the Log Collectors at the same time.
- D. Add Panorama Administrators to each Managed Collector.
Answer: C
Explanation:
You must upgrade all Log Collectors in a collector group at the same time to avoid losing log data
https://docs.paloaltonetworks.com/pan-os/10-2/pan-os-upgrade/upgrade-panorama/deploy- updates-to-firewalls-log-collectors-and-wildfire-appliances-using-panorama/deploy-an-update-to- log-collectors-when-panorama-is-internet-connected
NEW QUESTION # 117
A network administrator troubleshoots a VPN issue and suspects an IKE Crypto mismatch between peers. Where can the administrator find the corresponding logs after running a test command to initiate the VPN?
- A. Traffic logs
- B. System logs
- C. Configuration logs
- D. Tunnel Inspection logs
Answer: B
Explanation:
According to the Palo Alto Networks documentation, "To view IKE and IPSec Crypto profiles in the logs, filter the System log for eventid equal to vpn (Monitor > Logs > System)." Reference: https://docs.paloaltonetworks.com/pan-os/10-0/pan-os-admin/vpn/set-up-site-to-site-vpn/set-up-ike-crypto-profiles.html
NEW QUESTION # 118
An administrator creates an application-based security policy rule and commits the change to the firewall. Which two methods should be used to identify the dependent applications for the respective rule? (Choose two.)
- A. Review the App Dependency application list from the Commit Status view.
- B. Reference another application group containing similar applications.
- C. Use the show predefined xpath <value> command and review the output.
- D. Open the security policy rule and review the Depends On application list.
Answer: A,D
Explanation:
https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-admin/app-id/use-application-objects-in- policy/resolve-application-dependencies
NEW QUESTION # 119
Based on the image, what caused the commit warning?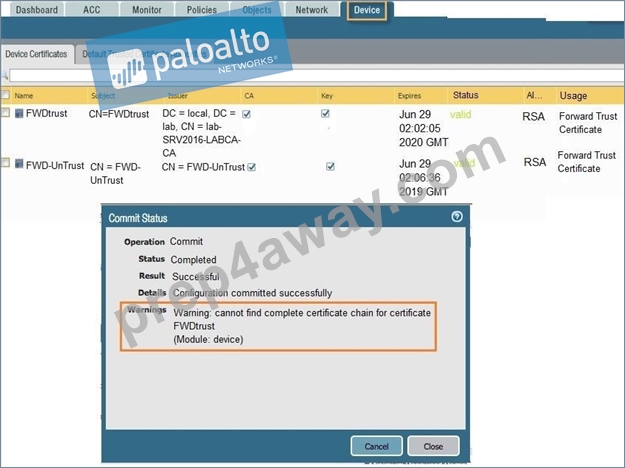
- A. The FWDtrust certificate has not been flagged as Trusted Root CA.
- B. The CA certificate for FWDtrust has not been imported into the firewall.
- C. SSL Forward Proxy requires a public certificate to be imported into the firewall.
- D. The FWDtrust certificate does not have a certificate chain.
Answer: D
NEW QUESTION # 120
Where can a service route be configured for a specific destination IP?
- A. Use Device > Setup > Services > Service Route Configuration > Customize > Destination
- B. Use Device > Setup > Services > Services
- C. Use Device > Setup > Services > Service Route Configuration > Customize > IPv4
- D. Use Network > Virtual Routers, select the Virtual Router > Static Routes > IPv4
Answer: C
Explanation:
Explanation
A service route is the path from the interface to the service on a server. By default, the firewall uses the management interface to communicate to various servers, including DNS, Email, Palo Alto Updates, User-ID agent, Syslog, Panorama, dynamic updates, URL updates, licenses, and AutoFocus. etc. Sometimes, it is necessary to use an alternative path other than Firewall management IP due to many restrictions. To configure service routes for non-predefined services, the destinationaddresses can be manually entered in the Destination section under Device > Setup > Services > Service Route Configuration > Customize1. Option A is incorrect because it is used to configure static routes for network traffic, not service routes for firewall services. Option B is incorrect because it is used to configure general service settings such as NTP server and proxy server, not service routes for specific destinations. Option D is incorrect because it is used to configure service routes for predefined services such as DNS and Syslog, not service routes for non-predefined services2.
NEW QUESTION # 121
Below are the steps in the workflow for creating a Best Practice Assessment in a firewall and Panorama configuration Place the steps in order.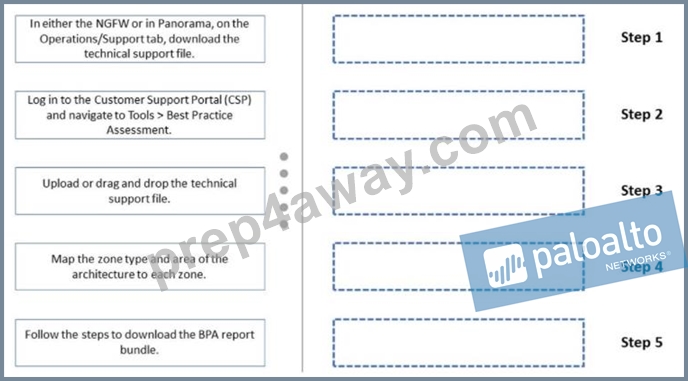
Answer:
Explanation: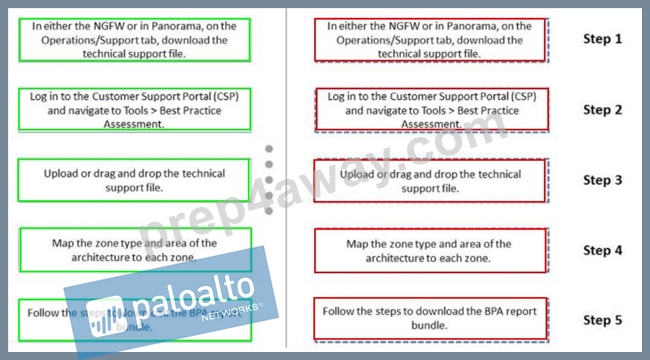
Reference:
https://www.paloaltonetworks.com/resources/videos/how-to-run-a-bpa
NEW QUESTION # 122
A network administrator wants to deploy SSL Forward Proxy decryption. What two attributes should a forward trust certificate have? (Choose two.)
- A. A private key
- B. A subject alternative name
- C. A certificate authority (CA) certificate
- D. A server certificate
Answer: B,D
Explanation:
Explanation
When deploying SSL Forward Proxy decryption, a forward trust certificate must have a subject alternative name (SAN) and be a server certificate. SAN is an extension to the X.509 standard that allows multiple domain names to be protected by a single SSL/TLS certificate. It is used to identify the domain names or IP addresses that the certificate should be valid for. A private key is also required but it is not mentioned in the options. A certificate authority (CA) certificate is not required as the forward trust certificate itself is a CA certificate.
NEW QUESTION # 123
In the screenshot above which two pieces ot information can be determined from the ACC configuration shown? (Choose two)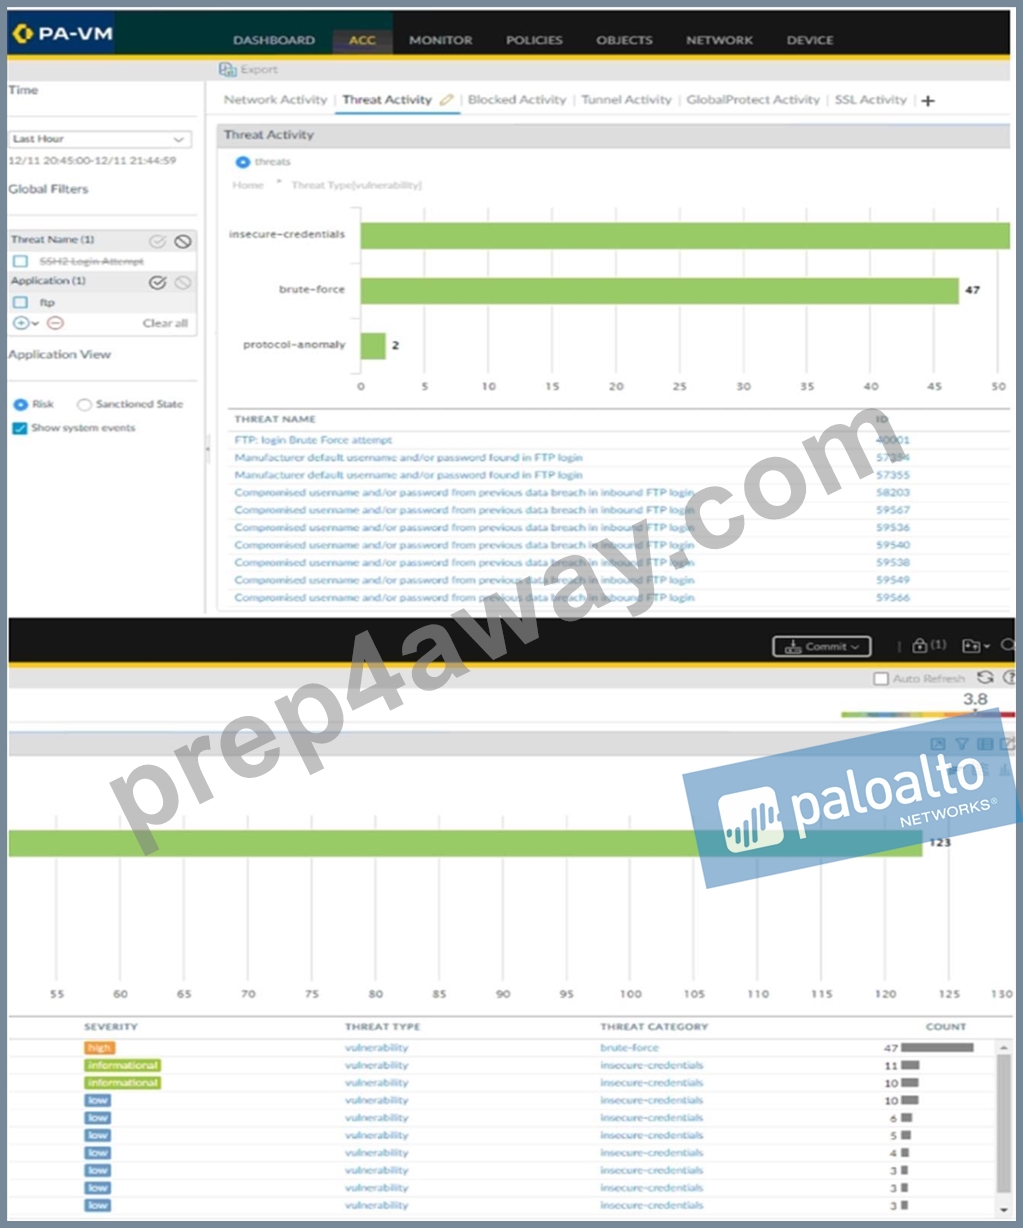
- A. The Network Activity tab will display all applications, including FTP.
- B. The ACC has been filtered to only show the FTP application
- C. Threats with a severity of "high" are always listed at the top of the Threat Name list
- D. Insecure-credentials, brute-force and protocol-anomaly are all a part of the vulnerability Threat Type
Answer: A,B
Explanation:
https://docs.paloaltonetworks.com/pan-os/10-2/pan-os-admin/threat-prevention/threat-signatures
NEW QUESTION # 124
When overriding a template configuration locally on a firewall, what should you consider?
- A. Only Panorama can revert the override
- B. Panorama will update the template with the overridden value
- C. Panorama will lose visibility into the overridden configuration
- D. The firewall template will show that it is out of sync within Panorama
Answer: C
NEW QUESTION # 125
Which method will dynamically register tags on the Palo Alto Networks NGFW?
- A. Restful API or the VMWare API on the firewall or on the User-ID agent or the read-only domain controller (RODC)
- B. XML-API or the VMware API on the firewall or on the User-ID agent or the CLI
- C. Restful API or the VMware API on the firewall or on the User-ID agent
- D. XML API or the VM Monitoring agent on the NGFW or on the User-ID agent
Answer: D
Explanation:
Reference:
https://docs.paloaltonetworks.com/pan-os/10-0/pan-os-admin/policy/monitor-changes-in-the-virtual-environmen
NEW QUESTION # 126
A network administrator is troubleshooting an issue with Phase 2 of an IPSec VPN tunnel The administrator determines that the lifetime needs to be changed to match the peer. Where should this change be made?
- A. IKE Crypto profile
- B. IKE Gateway profile
- C. IPSec Tunnel settings
- D. IPSec Crypto profile
Answer: D
NEW QUESTION # 127
To protect your firewall and network from single source denial of service (DoS) attacks that can overwhelm its packet buffer and cause legitimate traffic to drop, you can configure
- A. PBP (Packet Buffer Protection)
- B. PGP (Packet Gateway Protocol)
- C. BGP (Border Gateway Protocol)
- D. PBP (Protocol Based Protection)
Answer: A
Explanation:
https://docs.paloaltonetworks.com/pan-os/10-2/pan-os-admin/zone-protection-and-dos- protection/zone-defense/packet-buffer-protection Packet Buffer Protection defends your firewall and network from single session DoS attacks that can overwhelm the firewall's packet buffer and cause legitimate traffic to drop. Although you don't configure Packet Buffer Protection in a Zone Protection profile or in a DoS Protection profile or policy rule, Packet Buffer Protection defends ingress zones. While zone and DoS protection apply to new sessions (connections) and are granular, Packet Buffer Protection applies to existing sessions and is global.
NEW QUESTION # 128
What are the differences between using a service versus using an application for Security Policy match?
- A. Use of a "service" enables the firewall to take immediate action with the first observed packet based on port numbers. Use of an "application" allows the firewall to take immediate action if the port being used is a member of the application standard port list.
- B. Use of a "service" enables the firewall to take immediate action with the first observed packet based on port numbers. Use of an "application" allows the firewall to take action after enough packets allow for App-ID identification regardless of the ports being used
- C. Use of a "service" enables the firewall to take action after enough packets allow for App-ID identification
- D. There are no differences between "service" or "application". Use of an "application" simplifies configuration by allowing use of a friendly application name instead of port numbers.
Answer: A
NEW QUESTION # 129
A network administrator troubleshoots a VPN issue and suspects an IKE Crypto mismatch between peers.
Where can the administrator find the corresponding logs after running a test command to initiate the VPN?
- A. Traffic logs
- B. System logs
- C. Configuration logs
- D. Tunnel Inspection logs
Answer: B
Explanation:
Explanation
According to the Palo Alto Networks documentation, "To view IKE and IPSec Crypto profiles in the logs, filter the System log for eventid equal to vpn (Monitor > Logs > System)." References:https://docs.paloaltonetworks.com/pan-os/10-0/pan-os-admin/vpn/set-up-site-to-site-vpn/set-up-ike-c
NEW QUESTION # 130
Which three options are supported in HA Lite? (Choose three.)
- A. Session synchronization
- B. Synchronization of IPsec security associations
- C. Virtual link
- D. Active/passive deployment
- E. Configuration synchronization
Answer: B,D,E
Explanation:
"The PA-200 firewall supports HA Lite only. HA Lite is an active/passive deployment that provides configuration synchronization and some runtime data synchronization such as IPSec security associations. It does not support any session synchronization (HA2), and therefore does not offer stateful failover." Reference:
https://www.paloaltonetworks.com/documentation/80/pan-os/web-interface-help/device/device-high-availability/ha-lite
NEW QUESTION # 131
......
Introduction to Palo Alto Networks Certified Network Security Engineer PCNSE Exam
Palo Alto firewalls are Next Generation firewalls built from the ground up to address legacy firewalls issues. PCNSE exam dumps are a great way to start the Palo Alto Networks Certified Network Security Engineer (PCNSE PAN-OS) preparation by properly following and understanding each topic in the exam topics. PCNSE practice exams follows the syllabus in the Palo Alto and describe each topic to pass the exam the first time you take it. Also, the PCNSE practice test concentrates on the “learn by doing”, therefore, it is an exam with a lot of labs and configuration. Not just boring Power Points presentations. This guide is an instrument to get you on the same page with Palo Alto and understand the nature of the Palo Alto PCNSE exam.
The PCNSE exam should be taken by anyone who wishes to demonstrate a deep understanding of Palo Alto Networks technologies, including customers who use Palo Alto Networks products, value-added resellers, pre-sales system engineers, system integrators, and support staff.
The PCNSE exam focuses on the latest version of Palo Alto Networks' operating system, PAN-OS 10.0. PCNSE exam covers a variety of topics, including network security, threat prevention, and VPN technologies. PCNSE exam is intended for security professionals who have experience working with Palo Alto Networks' solutions and are looking to validate their skills and knowledge.
Get 100% Real Free PCNSE PAN-OS PCNSE Sample Questions: https://www.prep4away.com/Palo-Alto-Networks-certification/braindumps.PCNSE.ete.file.html
Download Palo Alto Networks PCNSE Exam Dumps to Pass Exam Easily: https://drive.google.com/open?id=1W_UX8G4SKNPn0Oz0f4JN2ztzA_nui4An