

(2021) PCNSA Dumps and Practice Test (170 Questions)
Guide (New 2021) Actual Palo Alto Networks PCNSA Exam Questions
Palo Alto Networks PCNSA Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
| Topic 8 |
|
| Topic 9 |
|
| Topic 10 |
|
NEW QUESTION 53
Match the network device with the correct User-ID technology.
Answer:
Explanation:
NEW QUESTION 54
What is considered best practice with regards to committing configuration changes?
- A. Disable the automatic commit feature that prioritizes content database installations before committing
- B. Validate configuration changes prior to committing
- C. Wait until all running and pending jobs are finished before committing
- D. Export configuration after each single configuration change performed
Answer: A
NEW QUESTION 55
How often does WildFire release dynamic updates?
- A. every 15 minutes
- B. every 60 minutes
- C. every 5 minutes
- D. every 30 minutes
Answer: C
Explanation:
Explanation/Reference:
Reference: https://docs.paloaltonetworks.com/pan-os/7-1/pan-os-new-features/wildfire-features/five-minute- wildfire-updates
NEW QUESTION 56
Which two security profile types can be attached to a security policy? (Choose two.)
- A. antivirus
- B. vulnerability
- C. DDoS protection
- D. threat
Answer: A,B
NEW QUESTION 57
Which administrator type utilizes predefined roles for a local administrator account?
- A. Role-based
- B. Device administrator
- C. Superuser
- D. Dynamic
Answer: D
Explanation:
Explanation/Reference: https://docs.paloaltonetworks.com/pan-os/8-0/pan-os-cli-quick-start/get-started-with-the-cli/give- administrators-access-to-the-cli/administrative-privileges?PageSpeed=noscript
NEW QUESTION 58
Which administrator type utilizes predefined roles for a local administrator account?
- A. Role-based
- B. Device administrator
- C. Superuser
- D. Dynamic
Answer: D
Explanation:
References:
NEW QUESTION 59
Given the image, which two options are true about the Security policy rules. (Choose two.)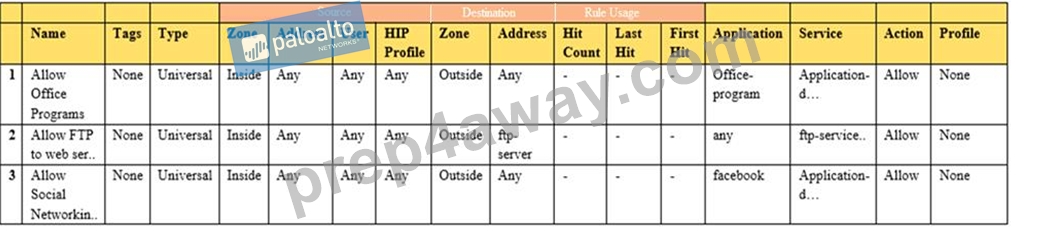
- A. The Allow Office Programs rule is using an Application Group
- B. The Allow Office Programs rule is using an Application Filter
- C. In the Allow Social Networking rule, allows all of Facebook's functions In the Allow FTP to web server rule, FTP is allowed using port based rule and not APP-ID.
- D. In the Allow FTP to web server rule, FTP is allowed using App-ID
Answer: B,C
NEW QUESTION 60
Which statements is true regarding a Heatmap report?
- A. It provides a set of questionnaires that help uncover security risk prevention gaps across all areas of network and security architecture.
- B. It runs only on firewall.
- C. It provides a percentage of adoption for each assessment area.
- D. When guided by authorized sales engineer, it helps determine te areas of greatest security risk.
Answer: C
NEW QUESTION 61
Based on the screenshot what is the purpose of the included groups?
- A. They contain only the users you allow to manage the firewall.
- B. They are only groups visible based on the firewall's credentials.
- C. They are groups that are imported from RADIUS authentication servers.
- D. They are used to map usernames to group names.
Answer: D
NEW QUESTION 62
Given the screenshot what two types of route is the administrator configuring? (Choose two )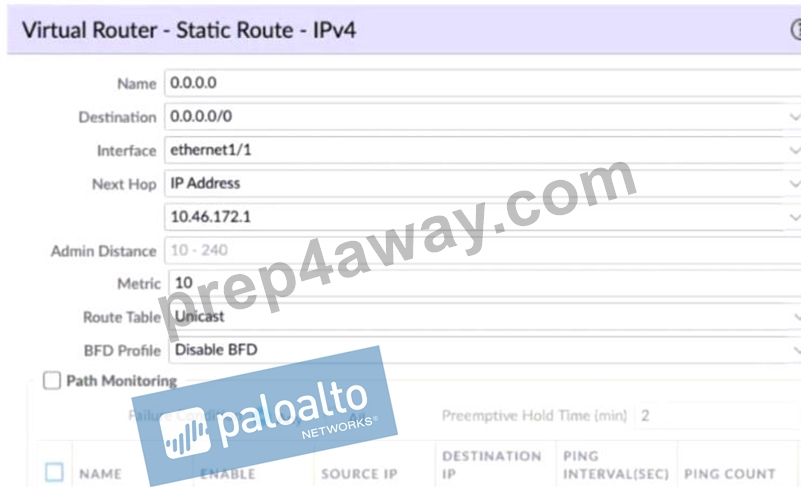
- A. static route
- B. default route
- C. OSPF
- D. BGP
Answer: B
NEW QUESTION 63
At which point in the app-ID update process can you determine if an existing policy rule is affected by an app-ID update?
- A. after connecting the firewall configuration
- B. after installing the update
- C. after clicking Check New in the Dynamic Update window
- D. after downloading the update
Answer: D
NEW QUESTION 64
Given the scenario, which two statements are correct regarding multiple static default routes? (Choose two.)
- A. Route with highest metric is actively used
- B. Route with lowest metric is actively used
- C. Path monitoring does not determine if route is useable
- D. Path monitoring determines if route is useable
Answer: B,D
NEW QUESTION 65
An administrator receives a global notification for a new malware that infects hosts. The infection will result in the infected host attempting to contact a command-and-control (C2) server. Which two security profile components will detect and prevent this threat after the firewall's signature database has been updated? (Choose two.)
- A. antivirus profile applied to outbound security policies
- B. vulnerability protection profile applied to outbound security policies
- C. URL filtering profile applied to outbound security policies
- D. anti-spyware profile applied to outbound security policies
Answer: C,D
Explanation:
References:
NEW QUESTION 66
Based on the screenshot presented which column contains the link that when clicked opens a window to display all applications matched to the policy rule?
- A. Apps Seen
- B. Service
- C. Name
- D. Apps Allowed
Answer: A
NEW QUESTION 67
Based on the screenshot presented which column contains the link that when clicked opens a window to display all applications matched to the policy rule?
- A. Apps Seen
- B. Service
- C. Name
- D. Apps Allowed
Answer: A
NEW QUESTION 68
......
PCNSA Exam Dumps Pass with Updated 2021 Certified Exam Questions: https://www.prep4away.com/Palo-Alto-Networks-certification/braindumps.PCNSA.ete.file.html
PCNSA Exam Questions - Real & Updated Questions PDF: https://drive.google.com/open?id=12elkmx8z-Ng4ix8g1RoQ4E0J0AJ5JlOY